AltPro
Organisation, project and task management behind a single sign-on I wrote rather than bought — two Spring services, one database, and a login the system owns.
- Role
- Full stack, auth server, deployment
- Year
- 2025
- Built with
- React
- TypeScript
- Spring Boot
- OAuth2
- MongoDB
- nginx
Two Spring Boot services behind one nginx: an authorization server built on Spring Authorization Server that issues OAuth2 and OIDC tokens, and a resource server that will not answer without a Bearer JWT. The React and TypeScript client never sees a password — it is redirected, comes back with an identity token, and calls the API with an access token that the API validates on its own.
Splitting the two was the point of the exercise. A single application with a login form on it can always be tempted into checking a session cookie somewhere it should be checking a token, and by the time there are two clients the temptation has already been given in to. With the issuer standing on its own the boundary is a network hop, and a mistake in it fails loudly.
The domain is deliberately hierarchical rather than flat — /api/orgs/{orgId}/projects/{projectId}/tasks — so that a task cannot be reached without proving the path to it. Organisations carry members and roles (ADMIN, MEMBER), projects belong to organisations, tasks to projects, comments to tasks, and an invitation is a first-class object rather than a nullable column. Both services share one MongoDB: the issuer keeps users, clients and consents, the API keeps the domain.
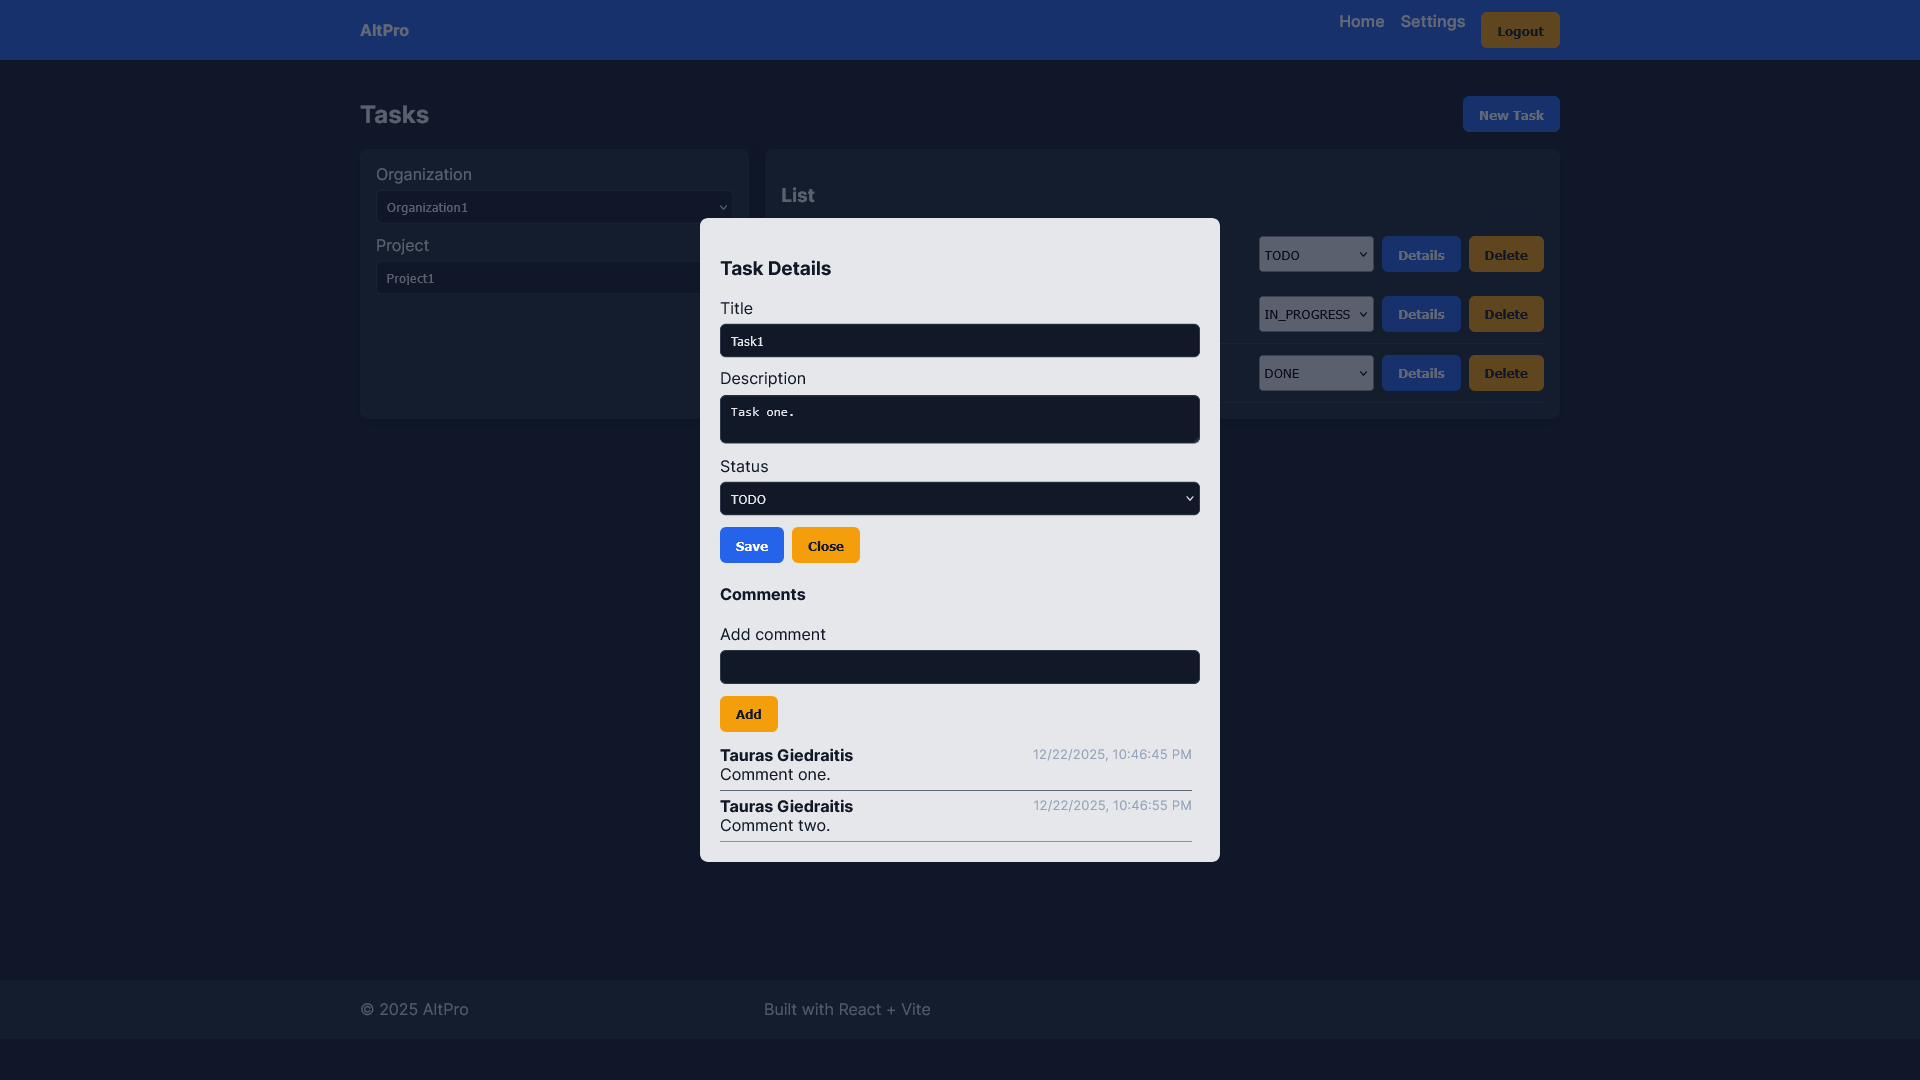
It ships with the description of itself. The whole API is written out as an OpenAPI document in the repository, and every screen was drawn as a wireframe before it was built — which is why the implementation screenshots and the wireframes still line up.
© 2026 Tauras Giedraitis · Kaunas, Lithuania · All rights reserved